Behavioural verification and SCA requirements
2019-08-04
Last update 2024-08-05
BLOCK0
source: https://eba.europa.eu/documents/10180/2622242/EBA+Opinion+on+SCA+elements+under+PSD2+.pdf
The banks approached individually to implement SCA - compliant methods, applying them in various variants and combinations. Some ways are costly; others process data that very sensitive. Specialists from UX pay attention to the fact that each additional interaction on the part of the client may reduce the convenience of using the website.
Can the requirement of strong authentication be solved more conveniently?
Some banks provide authentication via a mobile application, which, according to experts, seems to be a safer and cheaper option than text messages. However, it requires conscious user interaction.
And if it could be done much easier?
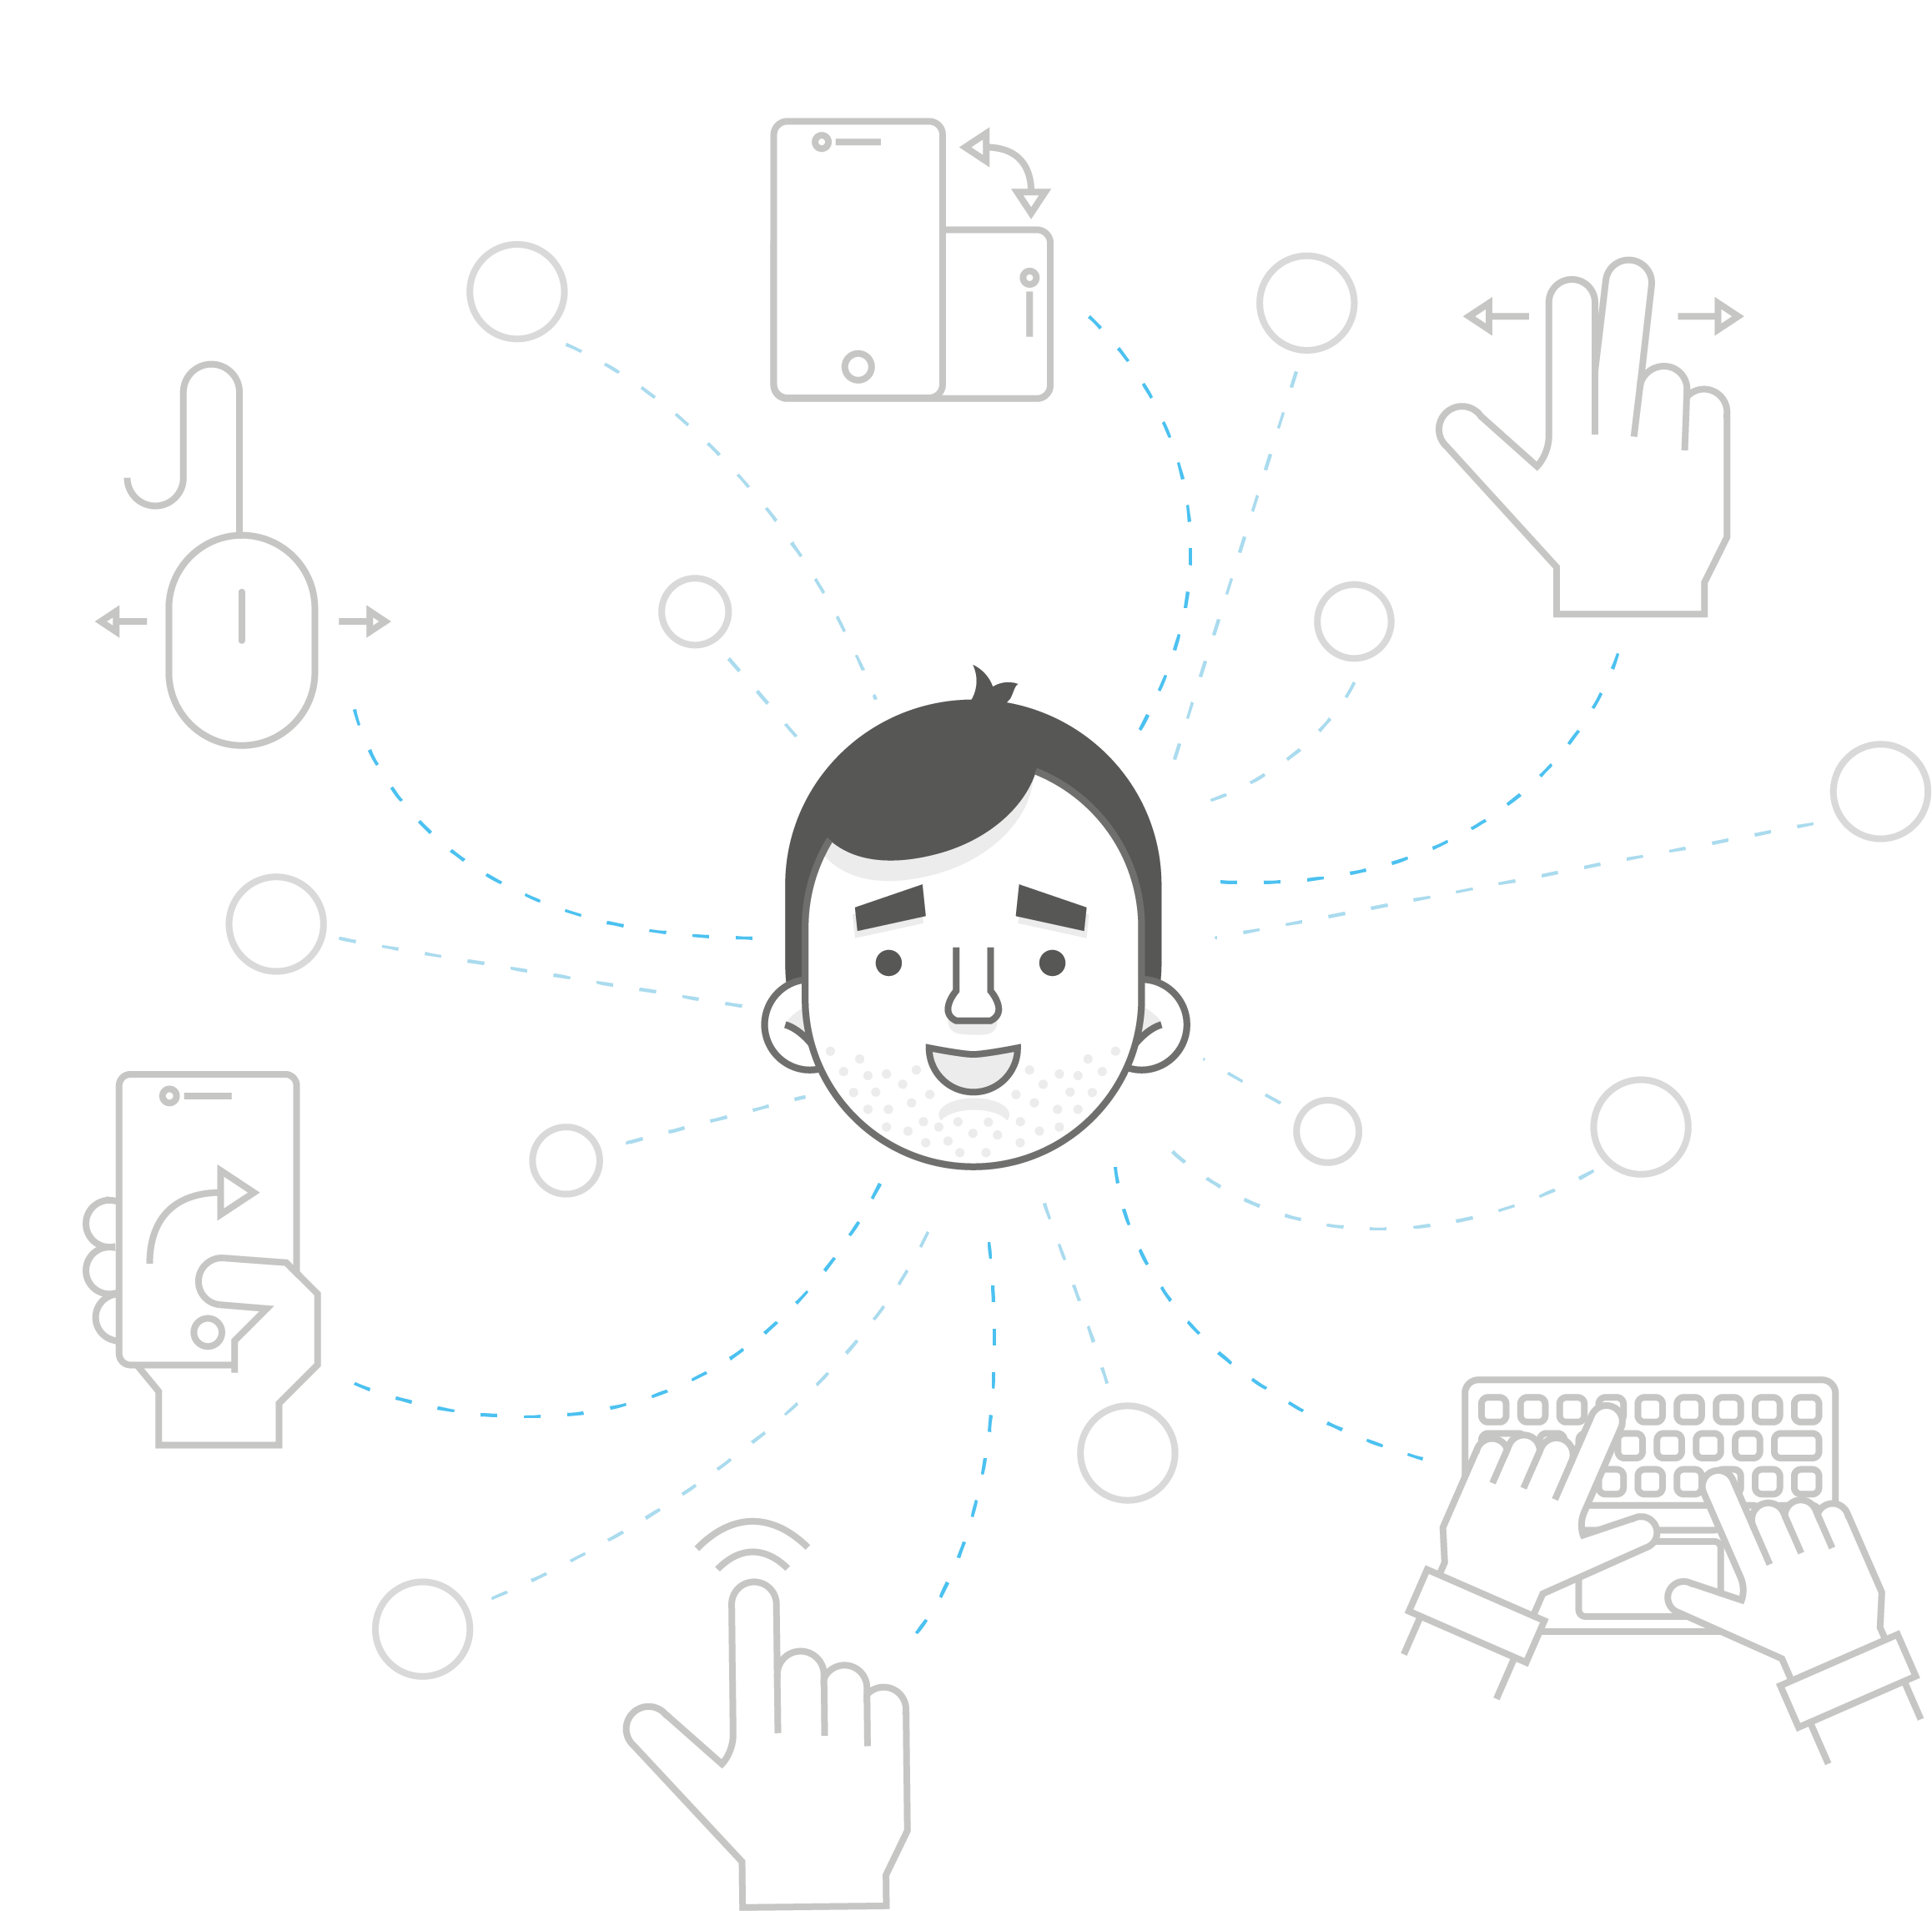
Digital Fingerprints is a product based on behavioural verification and is such a solution that can help in everyday use of electronic banking. It is an innovative security system that is observing human interaction with a computer. It is essential, among other things, how you type on the keyboard - how quickly you press the keys and in some way move the mouse - how fast and with what acceleration. Our priority when providing the service is the privacy and ethics of data processing. We do not collect data that is considered sensitive or uniquely identifying the user. We do not want to know what you are doing, but HOW you do it. Our solution is compliance with the GDPR and most importantly, with the SCA PSD2 requirement. The use of behavioural verification as the next layer of protection helps detect attacks such as sim card cloning and identity theft. It does not require additional user interaction and works in the background without affecting the comfort of using the website.
We allowed ourselves to create our own version of the table inspired by the one from the polish portal about cybersecurity niebezpiecznik.pl article
|
Behavioural verification |
|
|
Interaction with user |
Not required |
|
Stealing original |
Difficult |
|
Use after unauthorized access |
Difficult |
|
The time when client notice lost device |
No influence |
|
Extortion of code for future transaction |
Impossible |
|
Protection against MITB and MITM atacks |
High |
| Protection against malware on mobile devices |
High. Hacker must forge bahvioural manners of victim |
|
Attack over the network |
Impossible |